A plain-English look at what dataskydd för Copilot actually means in practice, and the specific checks UK organisations should run before wider rollout.

A plain-English look at what dataskydd för Copilot actually means in practice, and the specific checks UK organisations should run before wider rollout.
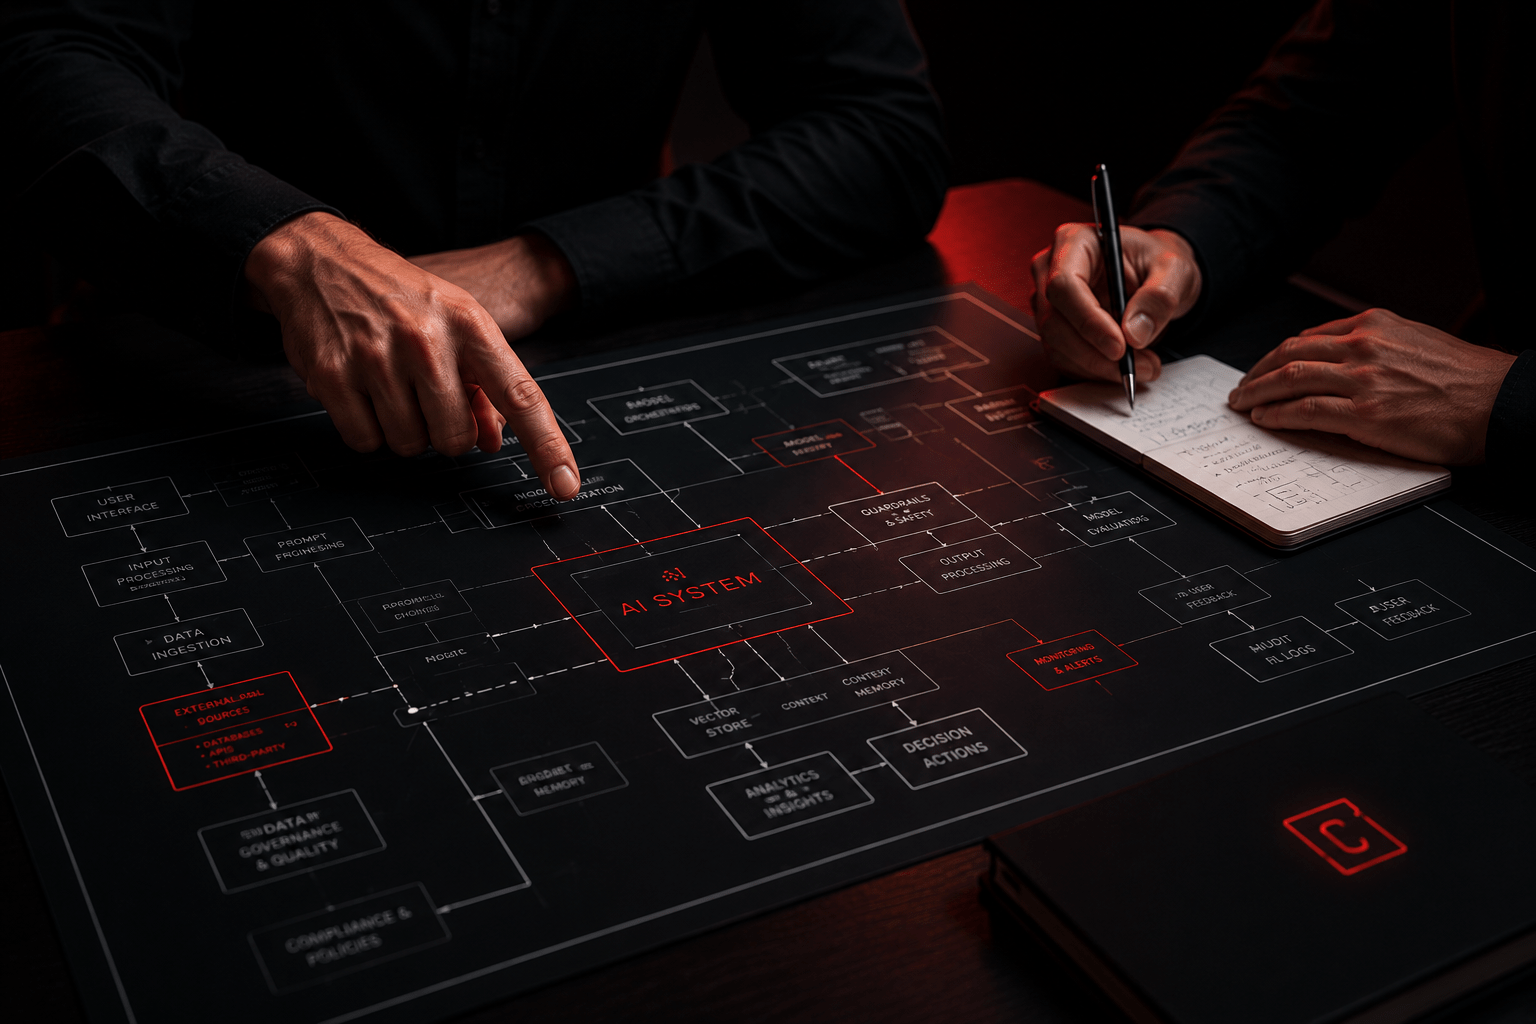
A practical look at how UK government departments can procure AI services while keeping compliance and governance intact from the outset.
Supplier assurance for AI tools needs to go well beyond a vendor questionnaire, and most organisations are missing the parts that matter most.

The ICO has been clear about how data protection law applies to AI, and organisations that treat it as a future concern are already behind.

Here because your preferred AI service is down? Claude down? ChatGPT down? One of the reasons to consider a local AI build. Adding AI to your workflow, then relying on a service that may not be there puts your business at risk. The more your staff rely on such tools, the greater that risk exposure […]

Procurement teams are signing AI vendor contracts without knowing what to ask, and the gaps that creates can surface as compliance failures, data incidents, or operational surprises months later.
The UK has chosen a different path to the EU on AI regulation, but that does not mean organisations can afford to wait and see.

AI sovereignty has moved from academic and policy discussions into practical governance conversations with unusual speed. It appears in procurement requirements, regulatory guidance, and board-level AI risk discussions with increasing frequency. Like most terms that achieve rapid adoption, it gets used to mean several related but distinct things, and that ambiguity creates confusion when organisations […]

Public AI vs private AI has become a standard feature of governance conversations, and it is a useful distinction when understood correctly. The problem is that many organisations apply it in ways that are either too simple to be accurate, or rest on assumptions about what “private AI” means that do not survive scrutiny. Getting […]

For organisations at the early stages of AI governance, policies and approved tool lists are the right starting point. They establish the framework, set expectations, and create the basic structure governance requires. For many organisations at this stage, that is enough. As AI adoption scales – more tools in use, more workflows incorporating AI, more […]


